Question 21 · 89 in bank
Refer to the exhibit.
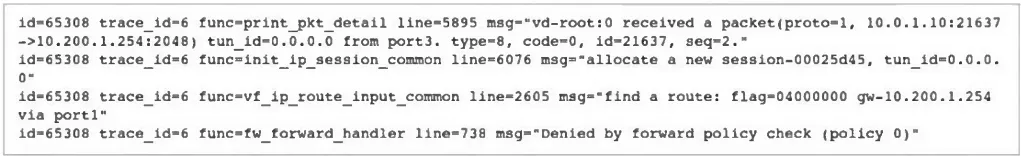
Why did FortiGate drop the packet?
Show answer
Answer: D
FCP — FortiGate 7.4 Administrator89 questions across 9 pages are complete and free, with no account or card.
89 questions in this bank
Free access · progress saved on this device
Refer to the exhibit.
Why did FortiGate drop the packet?
Answer: D
An administrator must enable a DHCP server on one of the directly connected networks on FortiGate. However, the administrator is unable to complete the process on the GUI to enable the service on the interface. In this scenario, what prevents the administrator from enabling DHCP service?
Answer: A
The 'DHCP server' option cannot be enabled/used on DMZ interfaces. For the interfaces with DMZ role, DHCP server and Security mode are not available (by design). If a DHCP server is required on that physical interface, change its role from DMZ to LAN, WAN, or Undefined.
Source: Adapted from community discussion — hecjoseroag
Refer to the exhibit.

Which algorithm does SD-WAN use to distribute traffic that does not match any of the SD-WAN rules?
Answer: A
https://docs.fortinet.com/document/fortigate/7.4.4/administration-guide/216765/implicit-rule Traffic is divided equally between the interfaces. Sessions that start at the same source IP address and go to the same destination IP address use the same path.
Source: Adapted from community discussion — lenriquereyes
Refer to the exhibit.

Review the intrusion prevention system (IPS) profile signature settings shown in the exhibit. What do you conclude when adding the FTP.Login.Failed signature to the IPS sensor profile?
Answer: D
D is correct. The action is set to Block at the top of the configuration setting. If it was set to default then the default action underneath for each signature will apply.
Source: Adapted from community discussion — JRKhan
The HTTP inspection process in web filtering follows a specific order when multiple features are enabled in the web filter profile. Which order must FortiGate use when the web filter profile has features such as safe search enabled?
Answer: D
The correct answer is: D. Static URL filter, FortiGuard category filter, and advanced filters When multiple web filtering features are enabled in FortiGate, the HTTP inspection process follows a specific sequence: Static URL Filter: This filter checks URLs against a predefined list of allowed or blocked URLs. FortiGuard Category Filter: This checks the category of the website using the FortiGuard database. Advanced Filters: These include features like -> "Safe Search" <-, YouTube EDU filtering, and other advanced filtering options. This order ensures efficient and layered filtering of web traffic based on various criteria.
Source: Adapted from community discussion — f3eb371
FortiGate is integrated with FortiAnalyzer and FortiManager. When a firewall policy is created, which attribute is added to the policy to improve functionality and to support recording logs to FortiAnalyzer or FortiManager?
Answer: D
An administrator configured a FortiGate to act as a collector for agentless polling mode. What must the administrator add to the FortiGate device to retrieve AD user group information?
Answer: D
"If FortiGate is acting as a collector for agentless polling mode, you must select Poll Active Directory Serverand configure the IP addresses and AD administrator credentials for each DC. FortiGate uses LDAP to query AD to retrieve user group information. For this to happen, you must add the LDAP server to the Poll Active Directory Server configuration."
Source: Adapted from community discussion — herlock_sholmes_2810
An administrator manages a FortiGate model that supports NTurbo. How does NTurbo enhance performance for flow-based inspection?
Answer: D
"NTurbo creates a special data path to redirect traffic from the ingress interface to the IPS engine, and from the IPS engine to the egress interface." Reference: FortiGate 7.4 Administrator Study Guide, page 201 (Inspection Modes Use Cases)
Source: Adapted from community discussion — herlock_sholmes_2810
Refer to the exhibit.

FortiGate has two separate firewall policies for Sales and Engineering to access the same web server with the same security profiles. Which action must the administrator perform to consolidate the two policies into one?
Answer: A
I feel like there should be 2 answers, like you have to enable Multiple Interface option first, and then select port1 and port2 in a single firewall policy
Source: Adapted from community discussion — Qwerty379
Refer to the exhibit, which shows a partial configuration from the remote authentication server.

Why does the FortiGate administrator need this configuration?
Answer: A
This configuration is specifically used to authenticate users belonging to the "Training" user group, as indicated by the Fortinet-Group-Name attribute.
Source: Adapted from community discussion — Billyon
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
FCP_FGT_AD-7.4 practice, question 21. 89 questions available.
Version 1.0.0. How we source questions