Question 241 · 647 in bank
What is one method of bypassing a system BIOS password?
Show answer
Answer: B
Computer Hacking Forensic Investigator (CHFI)647 questions across 65 pages are complete and free, with no account or card.
647 questions in this bank
Free access · progress saved on this device
What is one method of bypassing a system BIOS password?
Answer: B
What technique used by Encase makes it virtually impossible to tamper with evidence once it has been acquired?
Answer: B
A small law firm located in the Midwest has possibly been breached by a computer hacker looking to obtain information on their clientele. The law firm does not have any on-site IT employees, but wants to search for evidence of the breach themselves to prevent any possible media attention. Why would this not be recommended?
Answer: D
In the following directory listing:
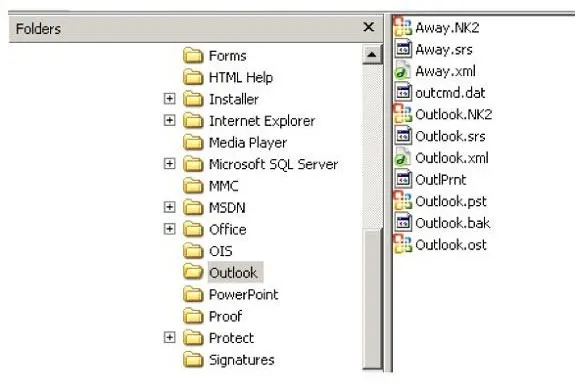
Which file should be used to restore archived email messages for someone using Microsoft Outlook?
Answer: D
Daryl, a computer forensics investigator, has just arrived at the house of an alleged computer hacker. Daryl takes pictures and tags all computer and peripheral equipment found in the house. Daryl packs all the items found in his van and takes them back to his lab for further examination. At his lab, Michael his assistant helps him with the investigation. Since Michael is still in training, Daryl supervises all of his work very carefully. Michael is not quite sure about the procedures to copy all the data off the computer and peripheral devices. How many data acquisition tools should Michael use when creating copies of the evidence for the investigation?
Answer: A
What is the smallest physical storage unit on a hard drive?
Answer: C
When needing to search for a website that is no longer present on the Internet today but was online few years back, what site can be used to view the website collection of pages?
Answer: D
Where does Encase search to recover NTFS files and folders?
Answer: B
What will the following command accomplish? dd if=/dev/xxx of=mbr.backup bs=512 count=1
Answer: A
Preparing an image drive to copy files to is the first step in Linux forensics. For this purpose, what would the following command accomplish? dcfldd if=/dev/zero of=/dev/hda bs=4096 conv=noerror, sync
Answer: A
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
312-49 practice, question 241. 647 questions available.
Version 1.0.0. How we source questions