Question 161 · 647 in bank
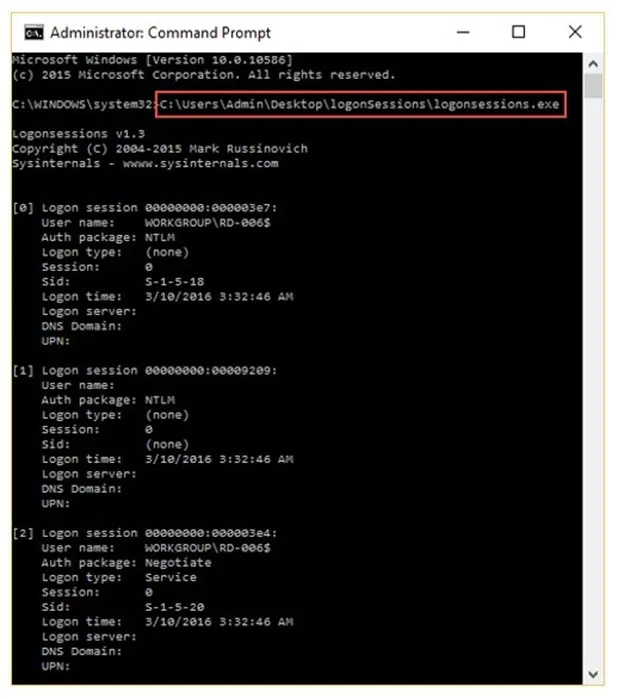
What is the investigator trying to analyze if the system gives the following image as output?
Show answer
Answer: B
Computer Hacking Forensic Investigator (CHFI)647 questions across 65 pages are complete and free, with no account or card.
647 questions in this bank
Free access · progress saved on this device
What is the investigator trying to analyze if the system gives the following image as output?
Answer: B
This organization maintains a database of hash signatures for known software.
Answer: C
As a part of the investigation, Caroline, a forensic expert, was assigned the task to examine the transaction logs pertaining to a database named Transfers. She used SQL Server Management Studio to collect the active transaction log files of the database. Caroline wants to extract detailed information on the logs, including AllocUnitId, page id, slot id, etc. Which of the following commands does she need to execute in order to extract the desired information?
Answer: D
The ____________________ refers to handing over the results of private investigations to the authorities because of indications of criminal activity.
Answer: D
%3cscript%3ealert("XXXXXXXX")%3c/script%3e is a script obtained from a Cross-Site Scripting attack. What type of encoding has the attacker employed?
Answer: C
Which of the following is a device monitoring tool?
Answer: A
From the site of Capsa: "Capsa is a portable network analyzer application for both LANs and WLANs which performs real-time packet capturing capability, 24x7 network monitoring, advanced protocol analysis, in-depth packet decoding, and automatic expert diagnosis." https://www.colasoft.com/capsa/ It says 24x7 network monitoring. Driver detective is a tool to list and update your Windows drivers. Think A is correct. But, truly tricky, indeed.
Source: Adapted from community discussion — Bodescu
During an investigation of an XSS attack, the investigator comes across the term "[a-zA-Z0-9\%]+" in analyzed evidence details. What is the expression used for?
Answer: A
[a-zA-Z0-9]+ is a pattern that matches against a string of any length, as long as the string contains only lowercase letters (a-z), uppercase letters (A-Z), or numerals (0-9).
Source: Adapted from community discussion — Selzar
Centralized binary logging is a process in which many websites write binary and unformatted log data to a single log file. What extension should the investigator look to find its log file?
Answer: C
Centralized binary logging is a server session property that, when enabled, configures logging for all of the URL groups under the server session. When centralized binary logging is enabled, data cannot be recorded or formatted for individual URL groups. The centralized binary logging log file has an Internet binary log (.ibl) file name extension. This file name extension ensures that text utilities do not try to open and read the central binary logging log file.
Source: Adapted from community discussion — BowerCarl
Printing under a Windows Computer normally requires which one of the following files types to be created?
Answer: C
What does the superblock in Linux define?
Answer: C
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
312-49 practice, question 161. 647 questions available.
Version 1.0.0. How we source questions