Question 571 · 888 in bank
The following is part of a log file taken from the machine on the network with the IP address of 192.168.1.106:
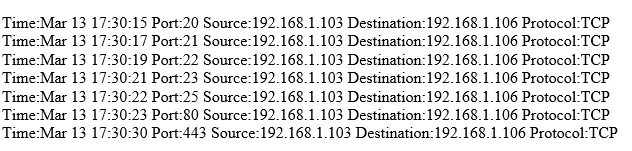
What type of activity has been logged?
Show answer
Answer: D
Certified Ethical Hacker (CEH)888 questions across 89 pages are complete and free, with no account or card.
888 questions in this bank
Free access · progress saved on this device
The following is part of a log file taken from the machine on the network with the IP address of 192.168.1.106:
What type of activity has been logged?
Answer: D
Taylor, a security professional, uses a tool to monitor her company's website, analyze the website's traffic, and track the geographical location of the users visiting the company's website. Which of the following tools did Taylor employ in the above scenario?
Answer: B
You are a cybersecurity consultant at SecureIoT Inc. A manufacturing company has contracted you to strengthen the security of their Industrial IoT (IIoT) devices used in their operational technology (OT)environment. They are concerned about potential attacks that could disrupt their production lines and compromise safety. They have an advanced firewall system in place, but you know this alone is not enough. Which of the following measures should you suggest to provide comprehensive protection for their IIoT devices?
Answer: D
MX record priority increases as the number increases. (True/False.)
Answer: B
Attacker Rony installed a rogue access point within an organization's perimeter and attempted to intrude into its internal network. Johnson, a security auditor, identified some unusual traffic in the internal network that is aimed at cracking the authentication mechanism. He immediately turned off the targeted network and tested for any weak and outdated security mechanisms that are open to attack. What is the type of vulnerability assessment performed by Johnson in the above scenario?
Answer: A
In an advanced digital security scenario, a multinational enterprise is being targeted with a complex series of assaults aimed to disrupt operations, manipulate data integrity, and cause serious financial damage. As the Lead Cybersecurity Analyst with CEH and CISSP certifications, your responsibility is to correctly identify the specific type of attack based on the following indicators: The attacks are exploiting a vulnerability in the target system's hardware, inducing misprediction of future instructions in a program's control flow. The attackers are strategically inducing the victim process to speculatively execute instructions sequences that would not have been executed in the absence of the misprediction, leading to subtle side effects. These side effects, which are observable from the shared state, are then utilized to infer the values of in-flight data. What type of attack best describes this scenario?
Answer: C
Which of the following statements about a zone transfer is correct? (Choose three.)
Answer: ACE
DNS uses TCP for Zone transfer and UDP for name, and queries either regular (primary) or reverse. Both TCP and UDP are port 53
Source: Adapted from community discussion — salei
Which of the following areas is considered a strength of symmetric key cryptography when compared with asymmetric algorithms?
Answer: B
You start performing a penetration test against a specific website and have decided to start from grabbing all the links from the main page. What is the best Linux pipe to achieve your milestone?
Answer: B
In the process of implementing a network vulnerability assessment strategy for a tech company, the security analyst is confronted with the following scenarios: 1) A legacy application is discovered on the network, which no longer receives updates from the vendor. 2) Several systems in the network are found running outdated versions of web browsers prone to distributed attacks. 3) The network firewall has been configured using default settings and passwords. 4) Certain TCP/IP protocols used in the organization are inherently insecure. The security analyst decides to use vulnerability scanning software. Which of the following limitations of vulnerability assessment should the analyst be most cautious about in this context?
Answer: A
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
312-50 practice, question 571. 888 questions available.
Version 1.0.0. How we source questions