Question 411 · 888 in bank
Which of the following is a common Service Oriented Architecture (SOA) vulnerability?
Show answer
Answer: D
Certified Ethical Hacker (CEH)888 questions across 89 pages are complete and free, with no account or card.
888 questions in this bank
Free access · progress saved on this device
Which of the following is a common Service Oriented Architecture (SOA) vulnerability?
Answer: D
You just set up a security system in your network. In what kind of system would you find the following string of characters used as a rule within its configuration?

Answer: D
Juliet, a security researcher in an organization, was tasked with checking for the authenticity of images to be used in the organization's magazines. She used these images as a search query and tracked the original source and details of the images, which included photographs, profile pictures, and memes. Which of the following footprinting techniques did Rachel use to finish her task?
Answer: C
An IT security engineer notices that the company’s web server is currently being hacked. What should the engineer do next?
Answer: A
In the above scenario, the company’s web server is hacked. As an IT security engineer, your first task is to unplug the network connection (cable) on the company’s web server from the router and modem in order to prevent further attacks.
Source: Adapted from community discussion — salei
Mary, a penetration tester, has found password hashes in a client system she managed to breach. She needs to use these passwords to continue with the test, but she does not have time to find the passwords that correspond to these hashes. Which type of attack can she implement in order to continue?
Answer: A
Cross-site request forgery involves:
Answer: C
Morris, a professional hacker, performed a vulnerability scan on a target organization by sniffing the traffic on the network to identify the active systems, network services, applications, and vulnerabilities. He also obtained the list of the users who are currently accessing the network. What is the type of vulnerability assessment that Morris performed on the target organization?
Answer: D
Which of the following network attacks takes advantage of weaknesses in the fragment reassembly functionality of the TCP/IP protocol stack?
Answer: A
A teardrop attack is a denial-of-service (DoS) attack that involves sending fragmented packets to a target machine. Since the machine receiving such packets cannot reassemble them due to a bug in TCP/IP fragmentation reassembly, the packets overlap one another, crashing the target network device.
Source: Adapted from community discussion — Joker20
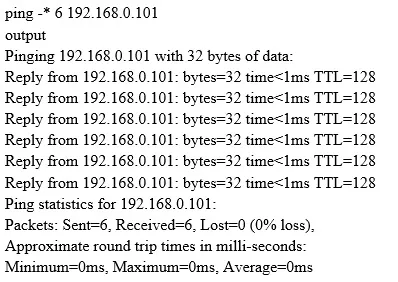
What does the option * indicate?
Answer: C
An Intrusion Detection System (IDS) has alerted the network administrator to a possibly malicious sequence of packets sent to a Web server in the network's external DMZ. The packet traffic was captured by the IDS and saved to a PCAP file. What type of network tool can be used to determine if these packets are genuinely malicious or simply a false positive?
Answer: A
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
312-50 practice, question 411. 888 questions available.
Version 1.0.0. How we source questions