Question 331 · 888 in bank
Peter is surfing the internet looking for information about DX Company. Which hacking process is Peter doing?
Show answer
Answer: B
Certified Ethical Hacker (CEH)888 questions across 89 pages are complete and free, with no account or card.
888 questions in this bank
Free access · progress saved on this device
Peter is surfing the internet looking for information about DX Company. Which hacking process is Peter doing?
Answer: B
Mike, a security engineer, was recently hired by BigFox Ltd. The company recently experienced disastrous DoS attacks. The management had instructed Mike to build defensive strategies for the company's IT infrastructure to thwart DoS/DDoS attacks. Mike deployed some countermeasures to handle jamming and scrambling attacks. What is the countermeasure Mike applied to defend against jamming and scrambling attacks?
Answer: D
When using Wireshark to acquire packet capture on a network, which device would enable the capture of all traffic on the wire?
Answer: A
A hacker is an intelligent individual with excellent computer skills and the ability to explore a computer's software and hardware without the owner's permission. Their intention can either be to simply gain knowledge or to illegally make changes. Which of the following class of hacker refers to an individual who works both offensively and defensively at various times?
Answer: C
You are using a public Wi-Fi network inside a coffee shop. Before surfing the web, you use your VPN to prevent intruders from sniffing your traffic. If you did not have a VPN, how would you identify whether someone is performing an ARP spoofing attack on your laptop?
Answer: A
Smart cards use which protocol to transfer the certificate in a secure manner?
Answer: A
The Extensible Authentication Protocol (EAP) is a protocol for wireless networks that expands the authentication methods used by the Point-to-Point Protocol (PPP), a protocol often used when connecting a computer to the internet. EAP is used on encrypted networks to provide a secure way to send identifying information to provide network authentication. It supports various authentication methods, including as token cards, smart cards, certificates, one-time passwords and public key encryption.
Source: Adapted from community discussion — Indushack
To determine if a software program properly handles a wide range of invalid input, a form of automated testing can be used to randomly generate invalid input in an attempt to crash the program. What term is commonly used when referring to this type of testing?
Answer: D
Lewis, a professional hacker, targeted the IoT cameras and devices used by a target venture-capital firm. He used an information-gathering tool to collect information about the IoT devices connected to a network, open ports and services, and the attack surface area. Using this tool, he also generated statistical reports on broad usage patterns and trends. This tool helped Lewis continually monitor every reachable server and device on the Internet, further allowing him to exploit these devices in the network. Which of the following tools was employed by Lewis in the above scenario?
Answer: C
From the two screenshots below, which of the following is occurring?
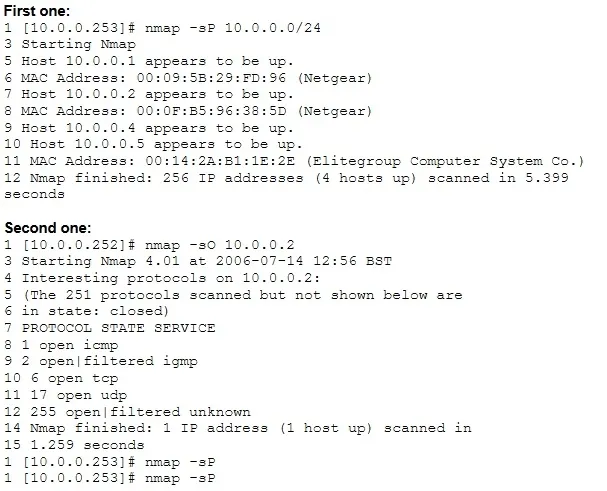
Answer: A
Answer A states the same information as Answer D does, but then also includes the correct information for the first scan, this is why A is correct.
Source: Adapted from community discussion — bleepbl0p
If you want only to scan fewer ports than the default scan using Nmap tool, which option would you use?
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
312-50 practice, question 331. 888 questions available.
Version 1.0.0. How we source questions