Question 361 · 393 in bank
A company’s engineers must ensure that it is difficult for competitors to determine how the company’s software works. Which of the following techniques can help achieve this objective?
Show answer
Answer: D
CompTIA SecurityX393 questions across 40 pages are complete and free, with no account or card.
393 questions in this bank
Free access · progress saved on this device
A company’s engineers must ensure that it is difficult for competitors to determine how the company’s software works. Which of the following techniques can help achieve this objective?
Answer: D
The accounts payable analyst receives a voicemail from the Chief Executive Officer (CEO), requesting that an invoice be paid. The voicemail provides wire transfer details that do not match the instructions on file. Which of the following is the most likely attack being employed?
Answer: C
As part of a security audit in the software development life cycle, a product manager must demonstrate and provide evidence of a complete representation of the code and modules used within the production-deployed application prior to the build. Which of the following best provides the required evidence?
Answer: A
During post-incident analysis of a recent website outage, an incident response team identifies the following commands that were run from a compromised internal machine:
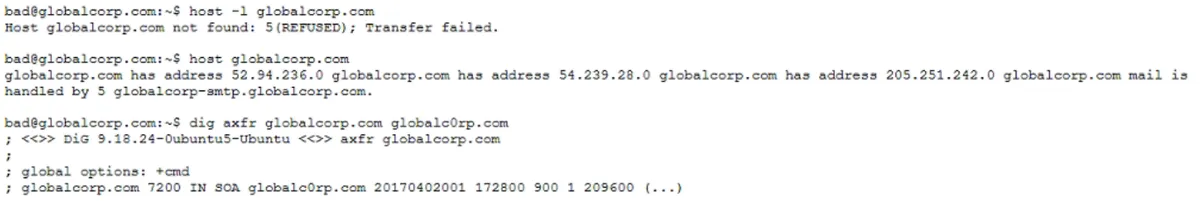
Which of the following should the team do?
Answer: D
The Chief Information Security Officer (CISO) asks the security team whether their SOC is receiving IoCs from an industry ISAC Which of the following is the most likely reason the CISO is interested in obtaining this information?
Answer: A
A security architect wants to integrate a new data source for its SOC team that meets the following requirements • Incident escalation should include specific data points • Clear remediation actions should be included for the incident response team • Timeliness and accuracy are the most important factors Which of the following is the best way to meet the architect's objective?
Answer: D
A security engineer receives the following findings from a recent security audit: • Data should be protected based on user permissions and roles • User action tracking should be implemented across the network • Digital identities should be validated across the data access workflow Which of the following is the first action the engineer should take to address the findings?
Answer: A
A security engineer discovers that some workstations are trying to establish communication with an unknown domain. The engineer compiles the following information:

Which of the following best describes this attack?
Answer: A
An IT team receives reports from an employee who is experiencing account lockouts. The analyst sees brute-force attempts from countries where the company does not have offices. Which of the following solutions would best address this issue?
Answer: A
A security officer is receiving alerts from a cloud service provider about a new wave of phishing campaigns. To prepare employees, the cloud service provider advises the company to make announcements and develop basic security competence. Which of the following solutions best aligns with the cloud service provider’s advice?
Answer: C
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CAS-005 practice, question 361. 393 questions available.
Version 1.0.0. How we source questions