Question 391 · 607 in bank
Which of the following actors attacking an organization is the most likely to be motivated by personal beliefs?
Show answer
Answer: C
CompTIA Security+607 questions across 61 pages are complete and free, with no account or card.
607 questions in this bank
Free access · progress saved on this device
Which of the following actors attacking an organization is the most likely to be motivated by personal beliefs?
Answer: C
Which of the following should a security team use to document persistent vulnerabilities with related recommendations?
Answer: B
A risk register is a document used by organizations to track and manage risks, including persistent vulnerabilities. It typically includes details about identified risks, their potential impact, likelihood, and related recommendations for mitigation or management.
Source: Adapted from community discussion — chasingsummer
An organization purchased a critical business application containing sensitive data. The organization would like to ensure that the application is not exploited by common data exfiltration attacks. Which of the following approaches would best help to fulfill this requirement?
Answer: B
The best approach to fulfill the requirement of preventing data exfiltration attacks on a critical business application is B. WAF (Web Application Firewall). A WAF provides targeted protection against various web-based threats, including those that could lead to data exfiltration, making it the most effective choice among the options listed
Source: Adapted from community discussion — Fourgehan
A company wants to improve the availability of its application with a solution that requires minimal effort in the event a server needs to be replaced or added. Which of the following would be the best solution to meet these objectives?
Answer: A
The correct answer is: A. Load balancing Explanation: Load balancing is an optimal solution for improving application availability. It distributes traffic across multiple servers, ensuring that if one server goes down or needs to be replaced, the load can be redistributed to the remaining servers without causing downtime. This approach requires minimal effort, as it can automatically redirect traffic to healthy servers without manual intervention, meeting the company's goal of minimal effort when adding or replacing servers.
Source: Adapted from community discussion — jbmac
A company is performing a risk assessment on new software the company plans to use. Which of the following should the company assess during this process?
Answer: A
A malicious actor is trying to access sensitive financial information from a company's database by intercepting and reusing log-in credentials. Which of the following attacks is the malicious actor attempting?
Answer: B
The correct answer is: B. On-path Explanation: An on-path attack (previously known as a "man-in-the-middle" attack) involves intercepting and potentially modifying the communication between two parties without their knowledge. In this case, the malicious actor is trying to intercept the log-in credentials to reuse them and gain unauthorized access to sensitive financial information from the company's database. This type of attack typically targets the communication channel, where credentials or sensitive data are transmitted.
Source: Adapted from community discussion — jbmac
A company is developing a business continuity strategy and needs to determine how many staff members would be required to sustain the business in the case of a disruption. Which of the following best describes this step?
Answer: A
A. Capacity planning Explanation: Capacity planning involves determining the staffing levels needed to sustain business operations during a disruption. This ensures that the organization has sufficient human resources to maintain essential functions and minimize downtime.
Source: Adapted from community discussion — SHADTECH123
A new employee accessed an unauthorized website. An investigation found that the employee violated the company's rules. Which of the following did the employee violate?
Answer: B
An AUP outlines the rules and guidelines for the acceptable use of company resources, including websites, networks, and devices. If the employee accessed an unauthorized website, they would be in violation of the AUP.
Source: Adapted from community discussion — 1f2b013
A systems administrator is reviewing the VPN logs and notices that during non-working hours a user is accessing the company file server and information is being transferred to a suspicious IP address. Which of the following threats is most likely occurring?
Answer: C
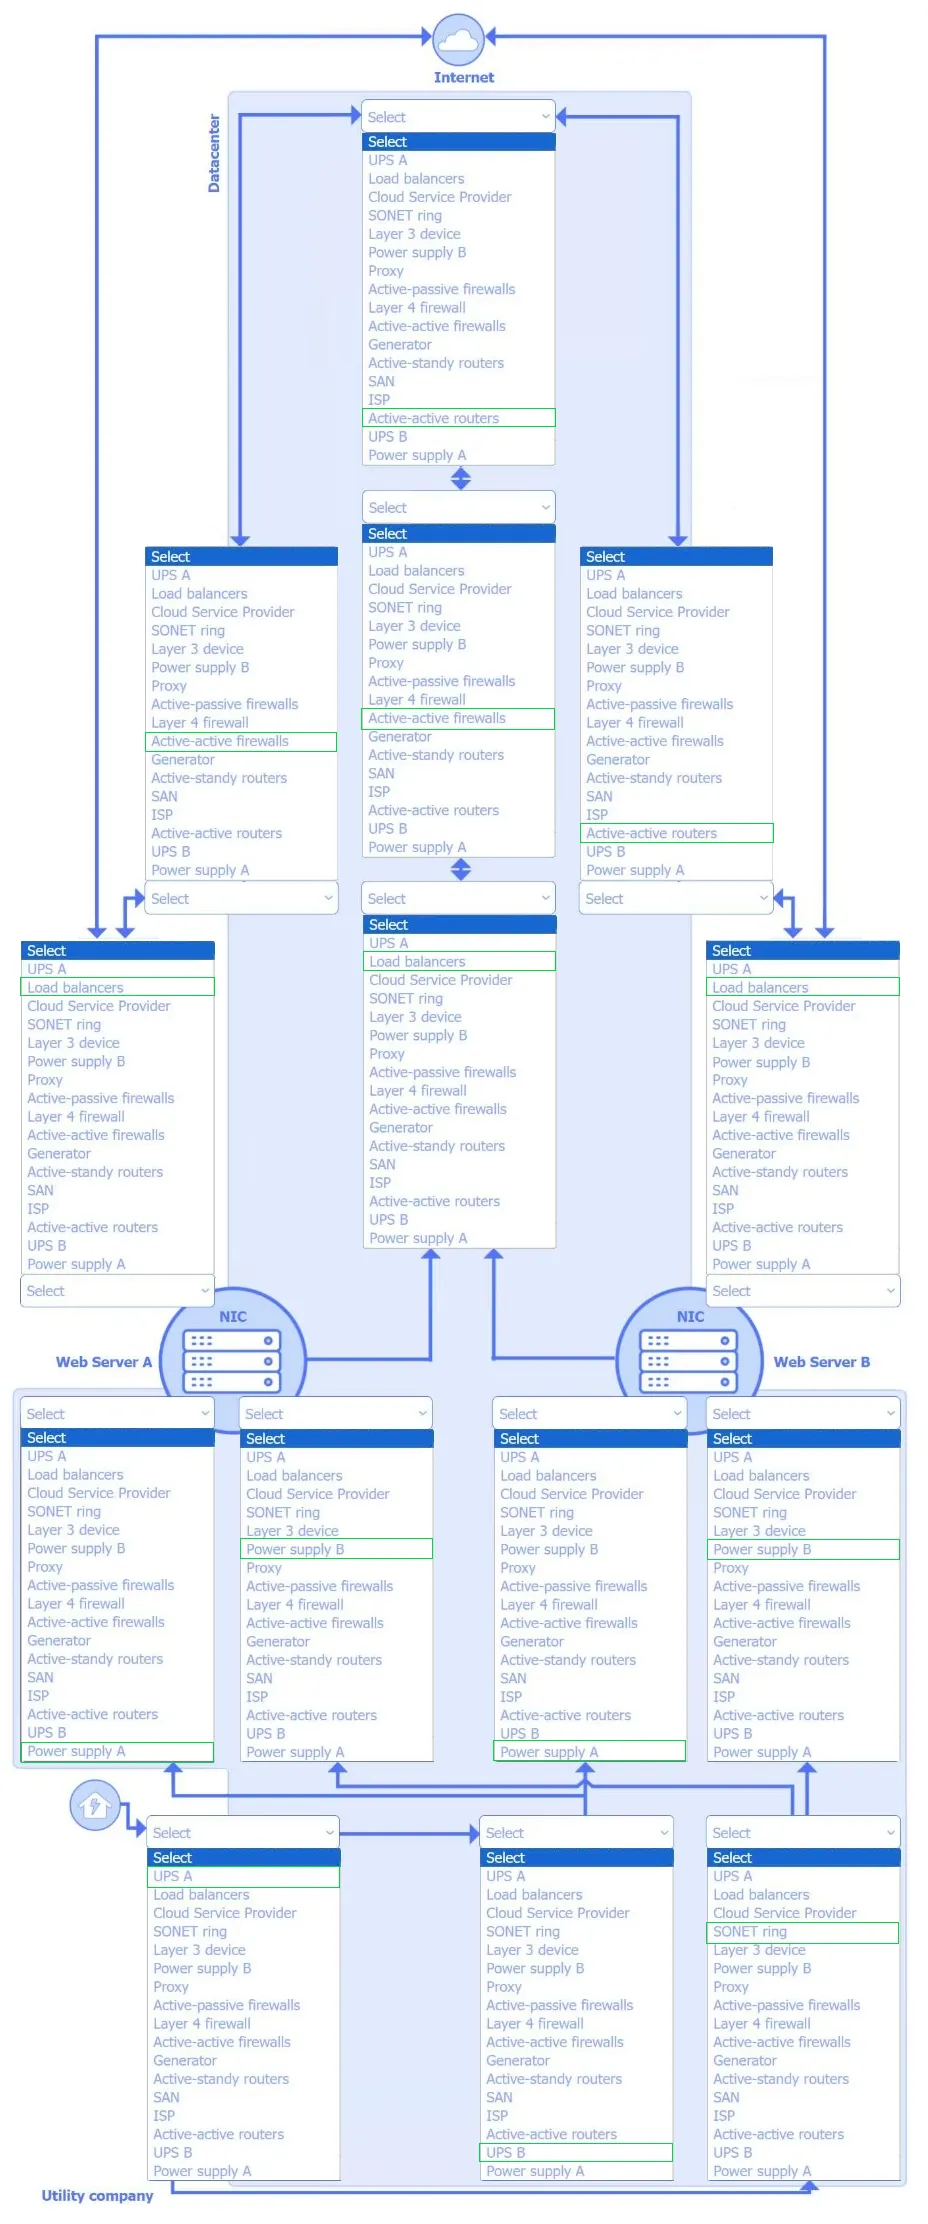
HOTSPOT - A security architect is tasked with designing a highly resilient, business-critical application. The application SLA is 99.999%. INSTRUCTIONS - Select the network, power, and server components for the appropriate locations to achieve application resiliency. A component should be selected for each location, and components may be selected more than once. If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
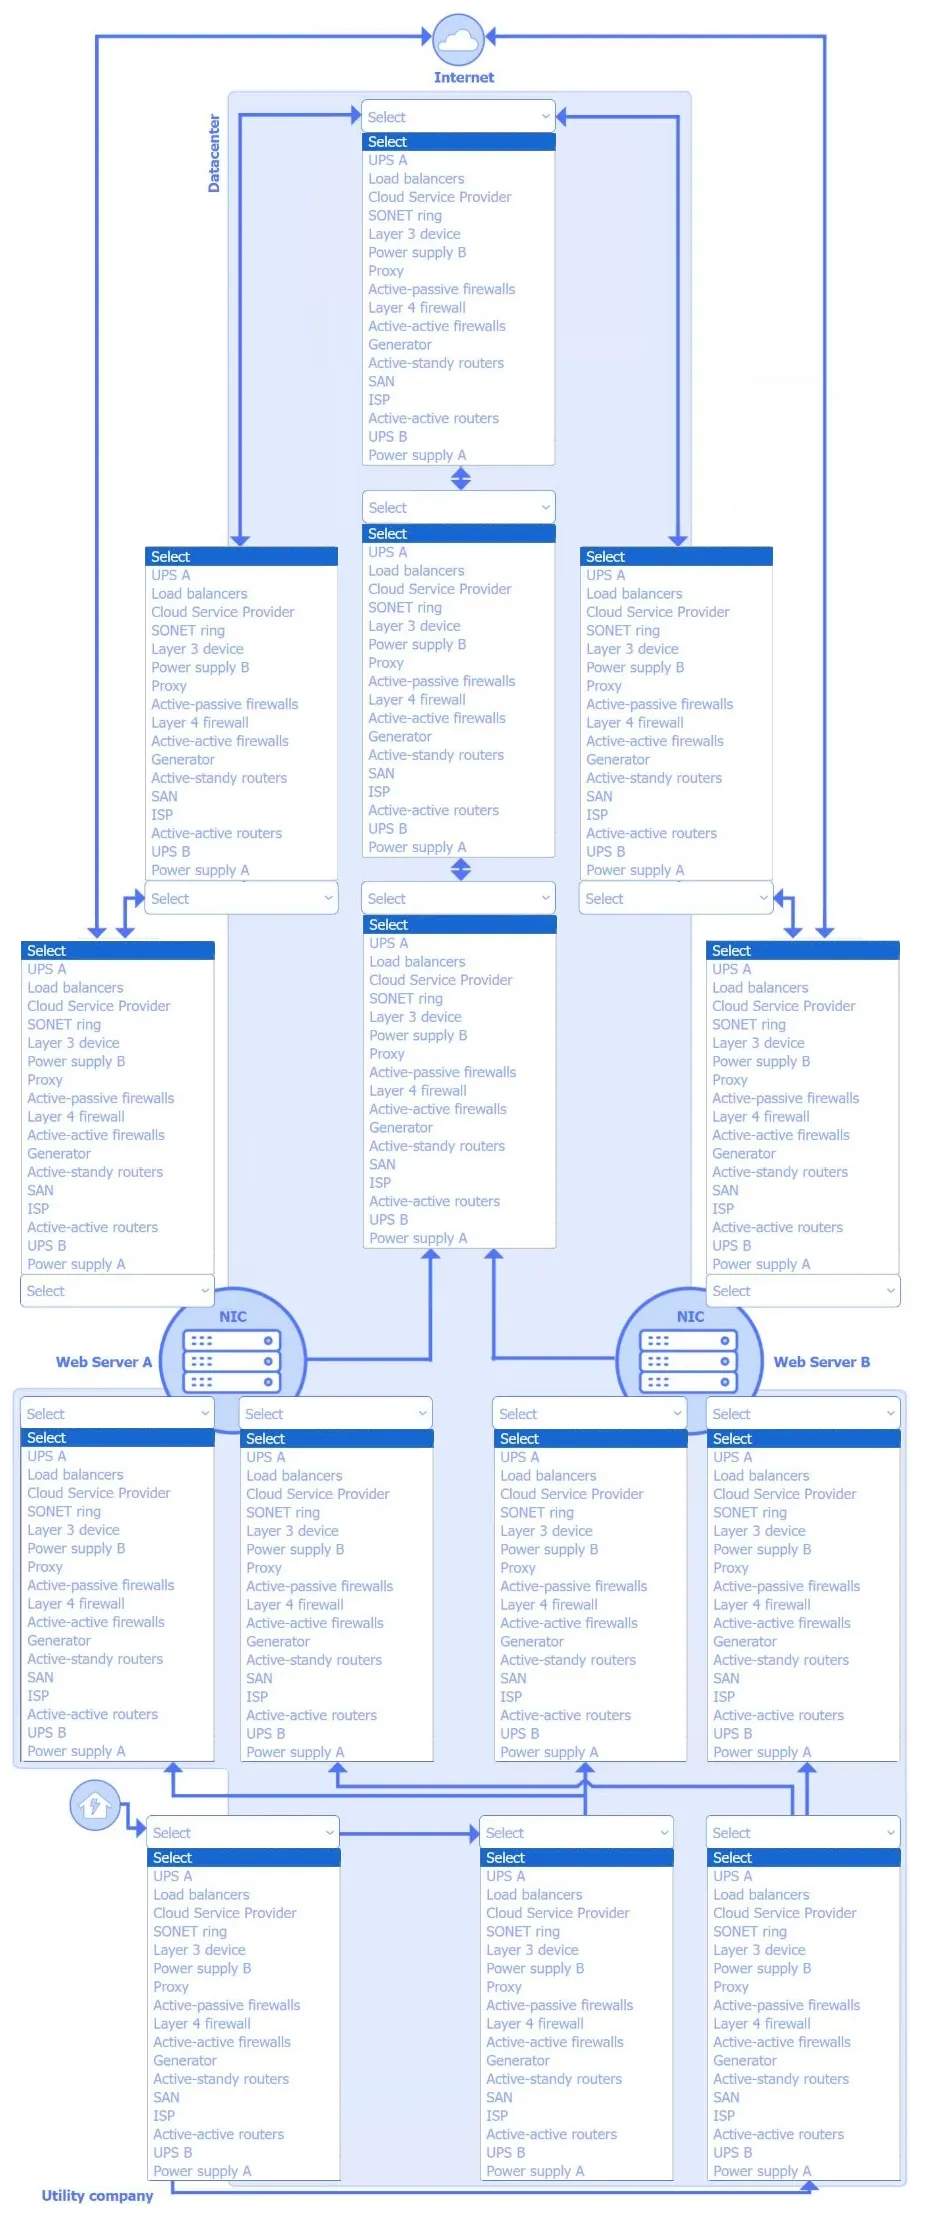
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Internet Firewall Firewall Layer 3 Device Active Router Layer 3 Device Active Router Load Balancer Web Server A Web Server B Power Supply A Power Supply A Power Supply B Power Supply B Generator UPS A UPS B
Source: Adapted from community discussion — AriGarcia
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
SY0-701 practice, question 391. 607 questions available.
Version 1.0.0. How we source questions