Question 61 · 335 in bank
A penetration tester is attempting to discover vulnerabilities in a company's web application. Which of the following tools would most likely assist with testing the security of the web application?
Show answer
Answer: D
CompTIA PenTest+335 questions across 34 pages are complete and free, with no account or card.
335 questions in this bank
Free access · progress saved on this device
A penetration tester is attempting to discover vulnerabilities in a company's web application. Which of the following tools would most likely assist with testing the security of the web application?
Answer: D
During a red-team exercise, a penetration tester obtains an employee's access badge. The tester uses the badge's information to create a duplicate for unauthorized entry. Which of the following best describes this action?
Answer: C
During an engagement, a penetration tester needs to break the key for the Wi-Fi network that uses WPA2 encryption. Which of the following attacks would accomplish this objective?
Answer: D
A penetration tester is researching a path to escalate privileges. While enumerating current user privileges, the tester observes the following output:
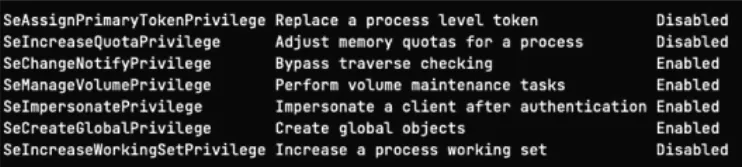
Which of the following privileges should the tester use to achieve the goal?
Answer: A
During a routine penetration test, the client's security team observes logging alerts that indicate several ID badges were reprinted after working hours without the appropriate authorization. Which of the following is the penetration tester most likely trying to do?
Answer: A
As part of an engagement, a penetration tester wants to maintain access to a compromised system after rebooting. Which of the following techniques would be best for the tester to use?
Answer: C
A penetration tester needs to scan a remote infrastructure with Nmap. The tester issues the following command: nmap 10.10.1.0/24 Which of the following is the number of TCP ports that will be scanned?
Answer: B
During an assessment, a penetration tester gains access to one of the internal hosts. Given the following command: schtasks /create /tn "Windows Update" /sc onlogon /tr “cmd.exe /c update.exe” Which of the following is the penetration tester trying to do with this code?
Answer: B
Given the following statements: Implement a web application firewall. Upgrade end-of-life operating systems. Implement a secure software development life cycle. In which of the following sections of a penetration test report would the above statements be found?
Answer: D
Which of the following is within the scope of proper handling and most crucial when working on a penetration testing report?
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PT0-003 practice, question 61. 335 questions available.
Version 1.0.0. How we source questions