Question 161 · 527 in bank
A security analyst receives an alert for suspicious activity on a company laptop. An excerpt of the log is shown below:
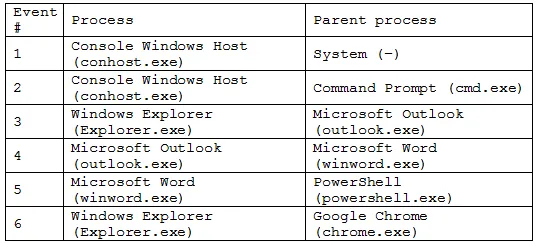
Which of the following has most likely occurred?
Show answer
Answer: A
Explanation
The sequence involving PowerShell and Microsoft Word (Event 5) strongly suggests the execution of a macro or script. This is a typical behavior of a malicious macro embedded in an Office document, which often uses PowerShell to perform further actions, such as downloading additional payloads or altering system settings.
Source: Adapted from community discussion — Chiniwini