Question 11 · 149 in bank
Which content filter condition checks to see if the “From: header” in the message is similar to any of the users in the content dictionary?
Show answer
Answer: C
Securing Email with Cisco Email Security Appliance (SESA)149 questions across 15 pages are complete and free, with no account or card.
149 questions in this bank
Free access · progress saved on this device
Which content filter condition checks to see if the “From: header” in the message is similar to any of the users in the content dictionary?
Answer: C
A network administrator notices that there are a high number of queries to the LDAP server. The mail logs show an entry “550 Too many invalid recipients | Connection closed by foreign host.” Which feature must be used to address this?
Answer: A
A is Correct. Directory Harvest Prevention. You can configure the appliance to combat directory harvest attacks using your LDAP directories. You can configure directory harvest prevention during the SMTP conversation or within the work queue. If the recipient is not found in the LDAP directory, you can configure the system to perform a delayed bounce or drop the message entirely. Consequently, spammers are not able to differentiate between valid and invalid email addresses. See Using LDAP For Directory Harvest Attack Prevention. https://www.cisco.com/c/en/us/td/docs/security/esa/esa11-1/user_guide/b_ESA_Admin_Guide_11_1/b_ESA_Admin_Guide_chapter_011010.html?bookSearch=true
Source: Adapted from community discussion — GVKD
What are two prerequisites for implementing undesirable URL protection in Cisco ESA? (Choose two.)
Answer: AC
Reference: https://www.cisco.com/c/en/us/td/docs/security/esa/esa12-0/user_guide/b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_chapter_01111.html
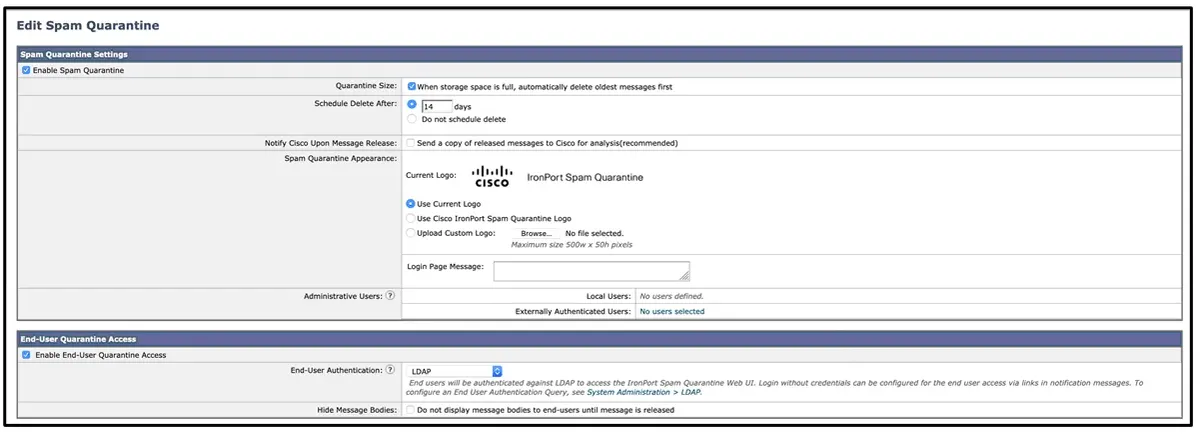
Refer to the exhibits. What must be done to enforce end user authentication before accessing quarantine?
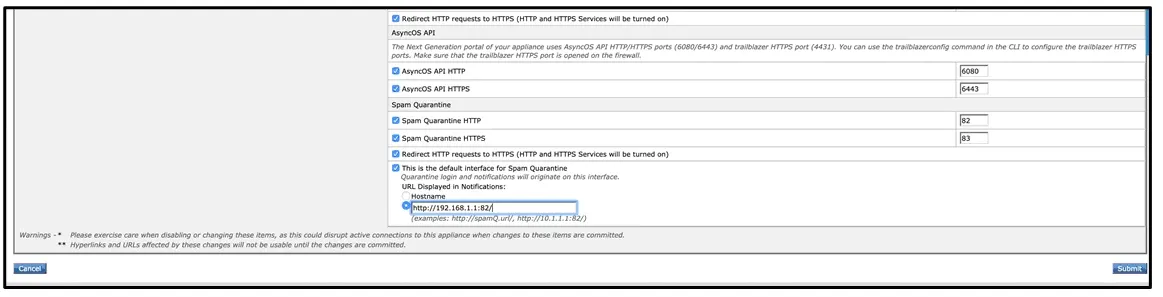
Answer: D
A is the correct answer. Look at "Authentication Options for End Users Accessing Spam Management Features" section. In the Spam Notifications settings, deselect or select Enable login without credentials for quarantine access. https://www.cisco.com/c/en/us/td/docs/security/esa/esa12-0/user_guide/b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_12_0_chapter_0100000.html
Source: Adapted from community discussion — mipetric93
An engineer is configuring a Cisco ESA for the first time and needs to ensure that any email traffic coming from the internal SMTP servers is relayed out through the Cisco ESA and is tied to the Outgoing Mail Policies. Which Mail Flow Policy setting should be modified to accomplish this goal?
Answer: B
Correct. Mail Flow Policies These are the policies that apply to the Sender Groups of the ESA, on the basis of which email traffic modulation is done. Mail Flow Policies always applies to traffic which is Incoming to the ESA irrespective of the email being an Inbound or Outbound one. The Mail Flow Policies works in the backend with regards to the selected Connection Behavior for that policy. The different Connection Behavior available in ESAs are: Accept Reject Relay TCP Refuse Continue https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/216842-understand-parameters-related-to-mail-fl.html
Source: Adapted from community discussion — GVKD
An organization wants to use its existing Cisco ESA to host a new domain and enforce a separate corporate policy for that domain. What should be done on the Cisco ESA to achieve this?
Answer: A
An engineer is configuring an SMTP authentication profile on a Cisco ESA which requires certificate verification. Which section must be configured to accomplish this goal?
Answer: A
What is the default primary email attribute used in a spam quarantine end-user authentication query when using LDAP authentication to an Active Directory server?
Answer: C
C is Correct. AsyncOS uses one of the following default query strings for the end-user authentication query: -Active Directory: (sAMAccountName={u}) -OpenLDAP: (uid={u}) -Unknown or Other: [Blank] https://www.cisco.com/c/en/us/td/docs/security/esa/esa14-0/user_guide/b_ESA_Admin_Guide_14-0/b_ESA_Admin_Guide_12_1_chapter_011011.html?bookSearch=true
Source: Adapted from community discussion — GVKD
Which components are required when encrypting SMTP with TLS on Cisco ESA when the sender requires TLS verification?
Answer: B
Correct. How to Encrypt SMTP Conversations using TLS: Step 1 Obtain an X.509 certificate and private key from a recognized certificate authority. https://www.cisco.com/c/en/us/td/docs/security/esa/esa14-0/user_guide/b_ESA_Admin_Guide_14-0/b_ESA_Admin_Guide_12_1_chapter_011001.html?bookSearch=true
Source: Adapted from community discussion — GVKD
The Cisco ESA is processing many messages that are sent to invalid recipients. To reduce this excessive processing, an engineer is preparing to use LDAP for recipient verification. Which two steps are required to accomplish this task? (Choose two.)
Answer: AC
A and C are Correct. Directory Harvest Attack Prevention within the SMTP Conversation You can prevent DHAs by entering only domains in the Recipient Access Table (RAT), and performing the LDAP acceptance validation in the SMTP conversation. To drop messages during the SMTP conversation, configure an LDAP server profile for LDAP acceptance. Then, configure the listener to perform an LDAP accept query during the SMTP conversation. Once you configure LDAP acceptance queries for the listener, you must configure DHAP settings in the mail flow policy associated with the listener. https://www.cisco.com/c/en/us/td/docs/security/esa/esa14-0/user_guide/b_ESA_Admin_Guide_14-0/b_ESA_Admin_Guide_12_1_chapter_011011.html?bookSearch=true#con_1163450
Source: Adapted from community discussion — GVKD
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
300-720 practice, question 11. 149 questions available.
Version 1.0.0. How we source questions