Question 421 · 654 in bank
Which solution is made from a collection of secure development practices and guidelines that developers must follow to build secure applications?
Show answer
Answer: D
Implementing and Operating Cisco Security Core Technologies (SCOR)654 questions across 66 pages are complete and free, with no account or card.
654 questions in this bank
Free access · progress saved on this device
Which solution is made from a collection of secure development practices and guidelines that developers must follow to build secure applications?
Answer: D
An engineer is deploying Cisco Advanced Malware Protection (AMP) for Endpoints and wants to create a policy that prevents users from executing a file named abc123456789.exe without quarantining that file. What type of Outbreak Control list must the SHA-256 hash value for the file be added to in order to accomplish this?
Answer: D
The correct answer is D. Blocked Application When deploying Cisco Advanced Malware Protection (AMP) for Endpoints, an engineer can create policies to prevent users from executing certain files without quarantining them. To do this, the SHA-256 hash value for the file must be added to a Blocked Application list in the AMP for Endpoints policy. A Blocked Application list is a type of Outbreak Control list that allows an organization to block specific files or applications, and prevent them from executing on endpoint devices. When a file or application is added to this list, it is blocked and cannot be executed, regardless of its reputation or other characteristics. This can be useful for preventing the execution of known malicious files or applications, or for blocking the execution of files or applications that are known to be vulnerable to exploitation. In this scenario, the SHA-256 hash value for the file named abc123456789.exe must be added to the Blocked Application list in the AMP for Endpoints policy.
Source: Adapted from community discussion — sull3y
What is the purpose of a NetFlow version 9 template record?
Answer: B
An organization is using DNS services for their network and want to help improve the security of the DNS infrastructure. Which action accomplishes this task?
Answer: D
D:o help improve the security of the DNS infrastructure, the organization can accomplish this task by configuring Cisco Umbrella and using DNSSEC for domain authentication to authoritative servers. Therefore, the correct answer is D. DNSSEC (Domain Name System Security Extensions) is a security feature that adds digital signatures to DNS data to ensure that the data is not modified or tampered with during transmission. By configuring Cisco Umbrella to use DNSSEC for domain authentication to authoritative servers, the organization can help improve the security of their DNS infrastructure.
Source: Adapted from community discussion — sull3y
Which Cisco security solution provides patch management in the cloud?
Answer: D
Im going with D on this one. ISE does not manage the cloud, Tetration (Secure Workloads) does. See link below: https://www.cisco.com/c/en/us/products/collateral/data-center-analytics/tetration-analytics/q-and-a-c67-737402.html The Cisco Secure Workload platform baselines the installed software packages, package version, patch level, and more for every workload. The platform maintains an up-to-date CVE data feed from multiple sources, including NIST and OS vendor data packs, which contain the latest vulnerability and exposure information. Using this, Secure Workload checks whether the software packages have known information security vulnerabilities. When a vulnerability is detected, complete details—including the severity and impact score—can be found. You can then quickly find all the servers with the same version of the package installed for patching and planning purposes.
Source: Adapted from community discussion — west33637
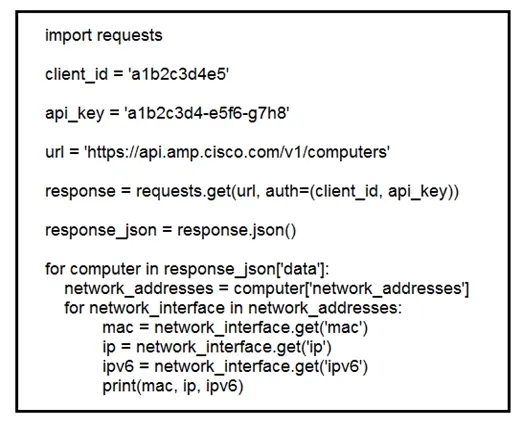
Refer to the exhibit. What does the API do when connected to a Cisco security appliance?
Answer: D
Which type of data exfiltration technique encodes data in outbound DNS requests to specific servers and can be stopped by Cisco Umbrella?
Answer: C
DRAG DROP - Drag and drop the common security threats from the left onto the definitions on the right. Select and Place:
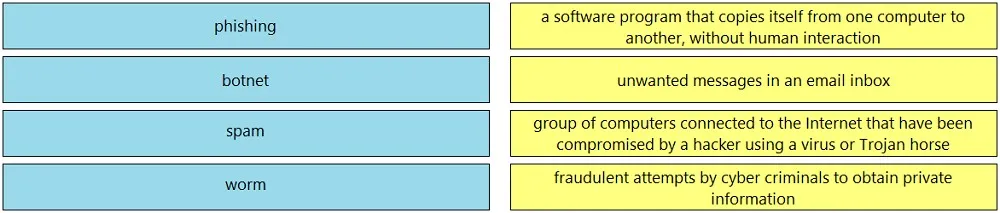
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below

Which solution is more secure than the traditional use of a username and password and encompasses at least two of the methods of authentication?
Answer: D
Which two capabilities does an MDM provide? (Choose two.)
Answer: BD
... and one more thing MDM was developed to manage light mobile device iOS'es - if you add to it MacOS, Windwos OS and other it is not MDM anymore, but UEM!! - it is Called MDM for a reason! Unified endpoint management Unified endpoint management (UEM) represents the integration and evolution of MDM and EMM. It solves more challenges associated with IoT, desktop or other mobile device security. UEM solutions can help enterprises secure and control the entire IT environment and its endpoints, such as smartphones, tablets, laptops and desktops. UEM solutions can also help secure their users’ personal data, apps, content and enterprise data. With an agile UEM system, enterprises can choose scalable solutions based on needs, whether those enterprise are covering a single operating system or various devices across different platforms, such as Apple iOS iPhone, Android, Microsoft Windows, macOS and Chrome OS. Mature UEM solutions are powered by machine learning and AI, which can help an enterprise’s IT department make quick security decision based on real-time data and analytics.
Source: Adapted from community discussion — Jessie45785
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
350-701 practice, question 421. 654 questions available.
Version 1.0.0. How we source questions