Question 211 · 385 in bank
A developer is designing a modern, distributed microservice enterprise application. The application will be integrating with other systems and focus on a large deployment, so control of API calls is necessary. What is the best practice to reduce application response latency and protect the application from excessive use?
Show answer
Answer: D
Explanation
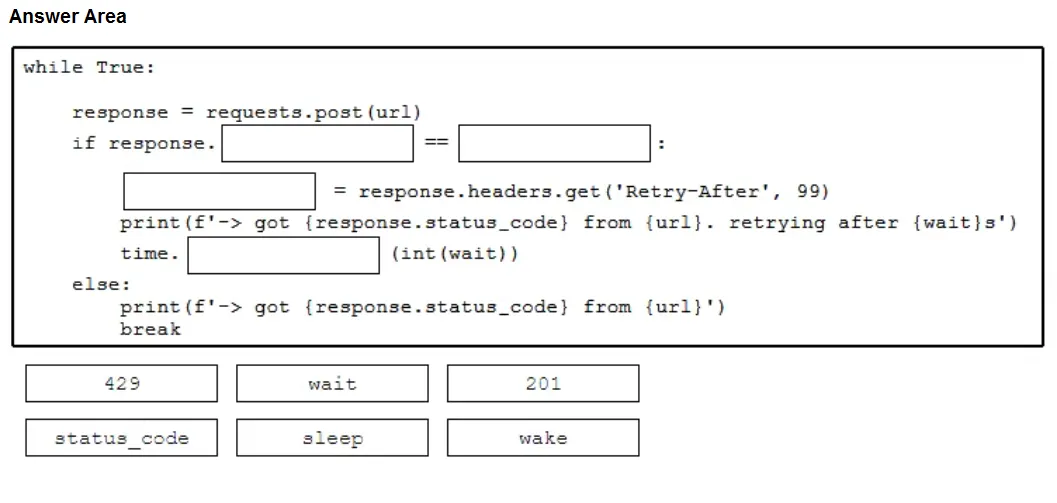
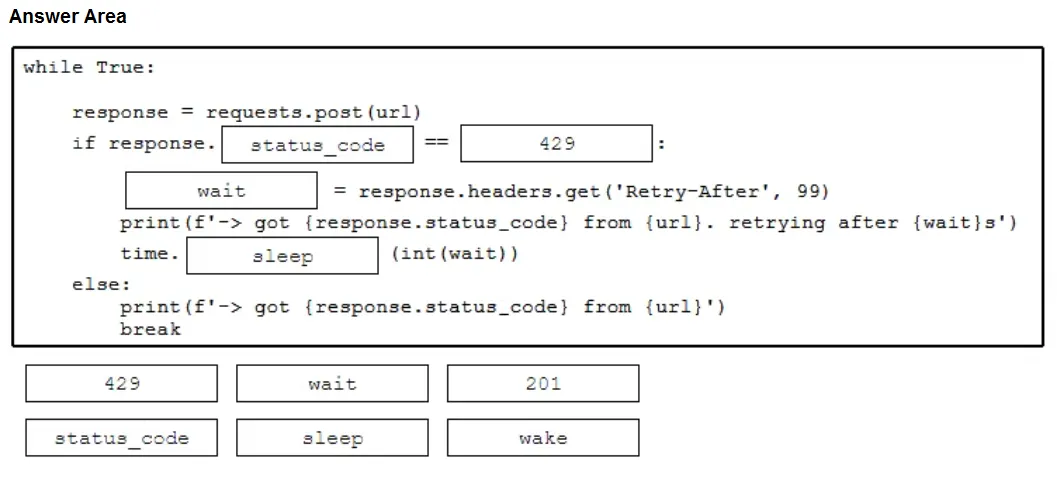
I agree that the best answer is **D. Implement rate limiting on the server side**. Rate limiting is a technique to control the number of requests that a client can make to a server in a given time period. It can help reduce application response latency and protect the application from excessive use by preventing **overload**, **abuse**, or **denial-of-service attacks**. Rate limiting can be implemented on the client side or the server side, or both. However, rate limiting on the client side is not very effective or reliable, because it depends on the client's implementation and honesty. A malicious or faulty client can bypass or ignore the rate limit and send too many requests to the server. Rate limiting on the server side is more secure and consistent, because it enforces the limit at the source and rejects any requests that exceed the limit.
Source: Adapted from community discussion — whipmuffin