Question 991 · 1334 in bank
What is a function of Cisco Advanced Malware Protection for a Next-Generation IPS?
Show answer
Answer: A
Cisco Certified Network Associate (CCNA)1,334 questions across 134 pages are complete and free, with no account or card.
1334 questions in this bank
Free access · progress saved on this device
What is a function of Cisco Advanced Malware Protection for a Next-Generation IPS?
Answer: A
What is a feature of WPA?
Answer: A
WPA also has a few other improvements over WEP, including the Temporal Key Integrity Protocol (TKIP) and the Message Integrity Code (MIC) WPA2 Enterprise uses IEEE 802.1X to deliver enterprise-grade authentication, and it was created specifically for use in businesses. WPA2-Personal is designed for use within the home and uses pre-shared keys (PSK). WPA3 uses Simultaneous Authentication of Equals (SAE) to provide stronger defenses against password guessing.
Source: Adapted from community discussion — AbdullahMohammad251
Which two practices are recommended for an acceptable security posture in a network? (Choose two.)
Answer: DE
A,D Use a cryptographic keychain to authenticate to network devices is correct, think Maintain network equipment in a secure location should be for physical not for security posture
Source: Adapted from community discussion — alejandro12
How does WPA3 improve security?
Answer: A
(A). It uses SAE (Simultaneous Authentication of Equals) for authentication. WPA3 replaces the pre-shared key (PSK) authentication method used in WPA2 with SAE, which provides stronger protection against offline dictionary and brute-force attacks. SAE allows users to securely authenticate with the network without revealing their passwords and protects against various authentication-related vulnerabilities.
Source: Adapted from community discussion — Cynthia2023
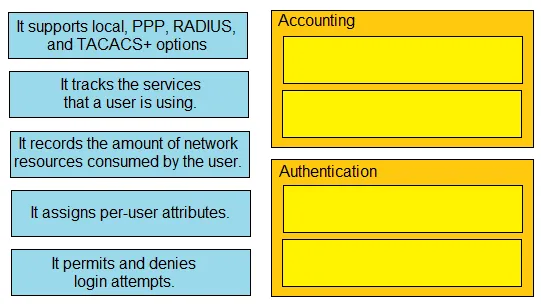
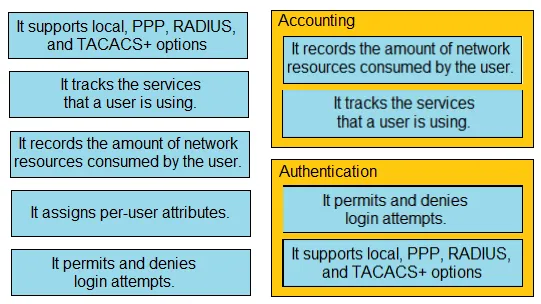
DRAG DROP - Drag and drop the statements about AAA from the left onto the corresponding AAA services on the right. Not all options are used. Select and Place:
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Per user attributes sounds like authorization. As each user could be configured to have different authorizations to different software and applications.
Source: Adapted from community discussion — RougePotatoe
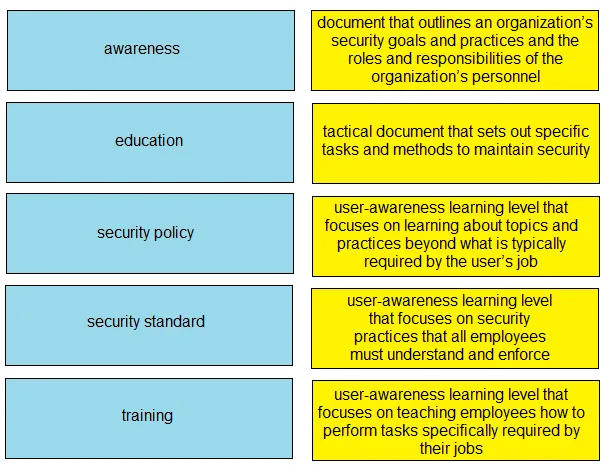
DRAG DROP - Drag and drop the elements of a security program from the left onto the corresponding descriptions on the right. Select and Place:
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
security policy security standard education awareness training It fits better takes it or leave it. The nuances is too blurry I wish cisco went out of business.
Source: Adapted from community discussion — RougePotatoe

A manager asks a network engineer to advise which cloud service models are used so employees do not have to waste their time installing, managing, and updating software that is only used occasionally. Which cloud service model does the engineer recommend?
Answer: D
Each model has the provider creating certain services. With IaaS, the provider does the: Networking, Hardware, Virtualisation. The client adds the O/S, Data, and Applications. With PaaS, the provider does the: Networking, Hardware, Virtualisation, and O/S. The client adds the Data, and Applications. With SaaS, the provider does the: Networking, Hardware, Virtualisation, O/S, Data and Application. The client just works on it.
Source: Adapted from community discussion — PaddyInNZ
Which IPsec transport mode encrypts the IP header and the payload?
Answer: D
https://www.cloudflare.com/en-gb/learning/network-layer/what-is-ipsec/ IPsec tunnel mode is used between two dedicated routers, with each router acting as one end of a virtual "tunnel" through a public network. In IPsec tunnel mode, the original IP header containing the final destination of the packet is encrypted, in addition to the packet payload. To tell intermediary routers where to forward the packets, IPsec adds a new IP header. At each end of the tunnel, the routers decrypt the IP headers to deliver the packets to their destinations. In transport mode, the payload of each packet is encrypted, but the original IP header is not. Intermediary routers are thus able to view the final destination of each packet — unless a separate tunneling protocol (such as GRE) is used.
Source: Adapted from community discussion — NewJeans
What is the default port-security behavior on a trunk link?
Answer: A
When you enable port security on a switch, by default only one MAC address can be learned. To allow more than one MAC address on a switch port simultaneously, use the command:port-security maximum .
Source: Adapted from community discussion — rijstraket
Which device separates networks by security domains?
Answer: B
B. Firewall A firewall is a device that separates networks by security domains. It acts as a barrier between different parts of a network, controlling the flow of traffic based on a set of rules. Firewalls are commonly used to enforce security policies, prevent unauthorized access, and protect networks from various threats. They are a key component in network security architectures.
Source: Adapted from community discussion — fd17639
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
200-301 practice, question 991. 1334 questions available.
Version 1.0.0. How we source questions